Frontend Code Security

Ways to raise the barrier against source theft: build modes, minification, hashing, obfuscation, and more.

Mar 12, 2021 · 1 min read · 72 Words · -Views -Comments · Programming
Frontend Development 🇨🇳 阅读中文版
Read with AI

Choose an AI assistant

ChatGPT Open in a new tab with the article link and prompt
Claude Copy the prompt, then open Claude

Open Claude
Trouble reading the article?

If the prompt is missing, copy the full prompt below into your AI assistant. If the AI cannot read the article, paste the visible passage you want to discuss and add your question.

Frontend resources ship to browsers/clients. How do we best protect JS and other assets to reduce risk of code theft in commercial projects? The goal is to raise the barrier and increase the cost of stealing.

Practical measures I’ve used:

  1. Build in production mode; strip debug info.

  2. Minify CSS/HTML/JS.

  3. Add hash to CSS class names.

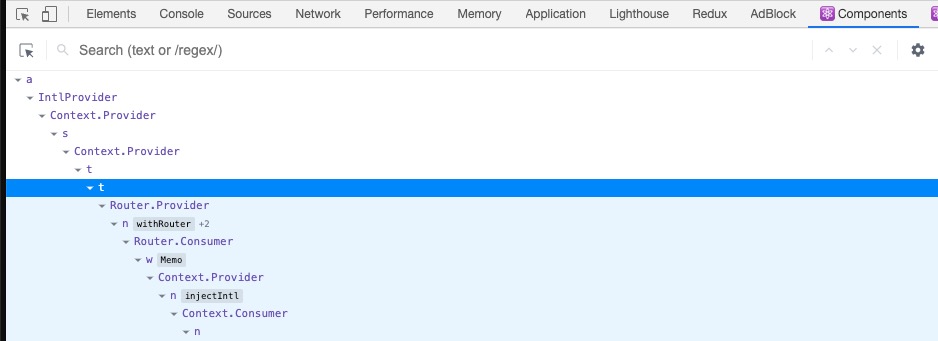
  4. Minify and mangle JS identifiers (e.g., via terser).

    • For example, using Terser

  5. Consider code obfuscation where appropriate.

Authors
Developer, digital product enthusiast, tinkerer, sharer, open source lover