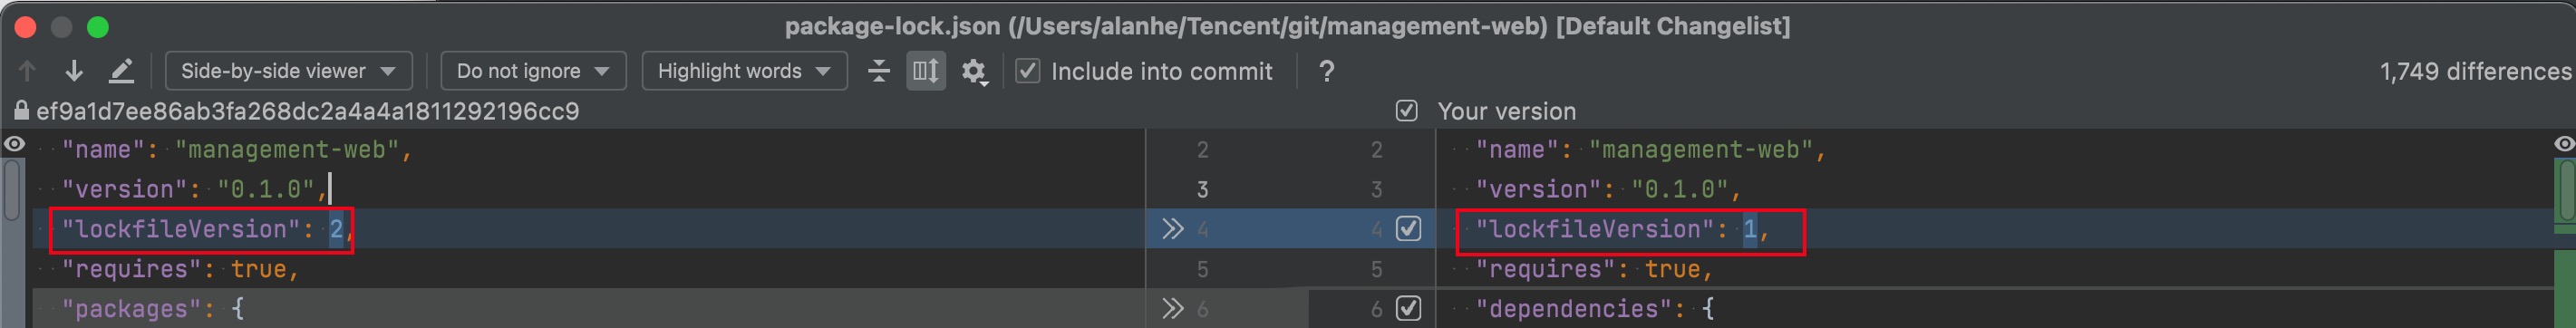
Encountered the following message when deploying frontend static resources in Docker: npm WARN read-shrinkwrap This version of npm is compatible with lockfileVersion@1, but package-lock.json was generated for lockfileVersion@2. I’ll try to do my best with it!
My local environment versions are as follows:
- node v14.17.0
- npm v7.x
After researching on Google, I found the cause. Different npm versions correspond to different lock file versions, with one specific manifestation being the different values of the lockfileVersion field. For example, npm v6 has lockfileVersion 1, while v7 has lockfileVersion 2.
In my case, the package-lock.json file was generated locally using npm v7, but during Docker deployment, I was using the built-in npm (v6) that comes with Node v14.17.0 for package installation, which caused this warning message.
The solution is to change npm to v6 locally and regenerate the lock file. Alternatively, you can control the npm version to v7 in Docker.

